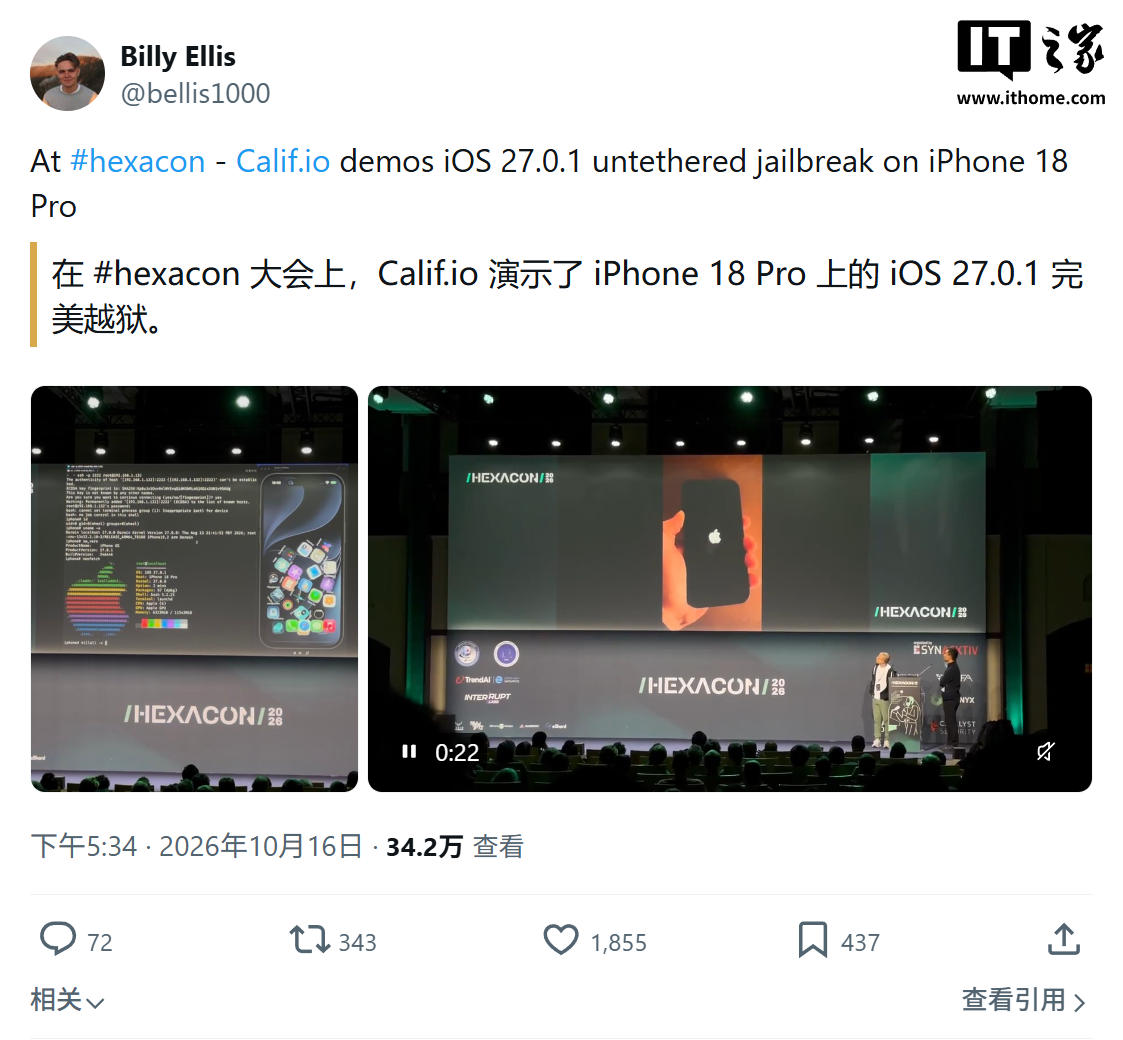
On October 17th, according to a post by technology media decrypt, at the Hexacon Security Conference held in Paris yesterday (October 16th), security company Calif.io publicly demonstrated a "perfect jailbreak" on a iPhone model running iOS version 27.0.1. After restarting, the device was still able to maintain the highest level of privileges.
IT Note: Jailbreaking refers to bypassing Apple's restrictions such as signature verification, app sandboxing, and protected startup chains for iOS, allowing users to gain the highest level of system permissions. This enables them to install non-App Store applications, access the entire file system, deeply customize the system interface, and even delete pre-installed software.
Unlike regular jailbreaks that require reconnection to the computer or reactivation of the vulnerability, "perfect jailbreak" ( untethered jailbreak ) refers to a state where the jailbroken condition persists even after the device is restarted.
During the live demonstration, after restarting the phone and unlocking it with a regular password, the researchers directly opened a session with the username root to access SSH. The terminal information confirmed that the system version was iOS 27.0.1.
The media pointed out that the security design of modern iPhone is extremely complex. Attackers usually need to exploit multiple vulnerabilities in sequence, first escape from the application sandbox, then take control of the kernel, and bypass hardware-level protections such as pointer authentication codes. To continue retaining their privileges after a restart, they also have to overcome Apple's verification of the startup code. Therefore, this demonstration has drawn a lot of attention.
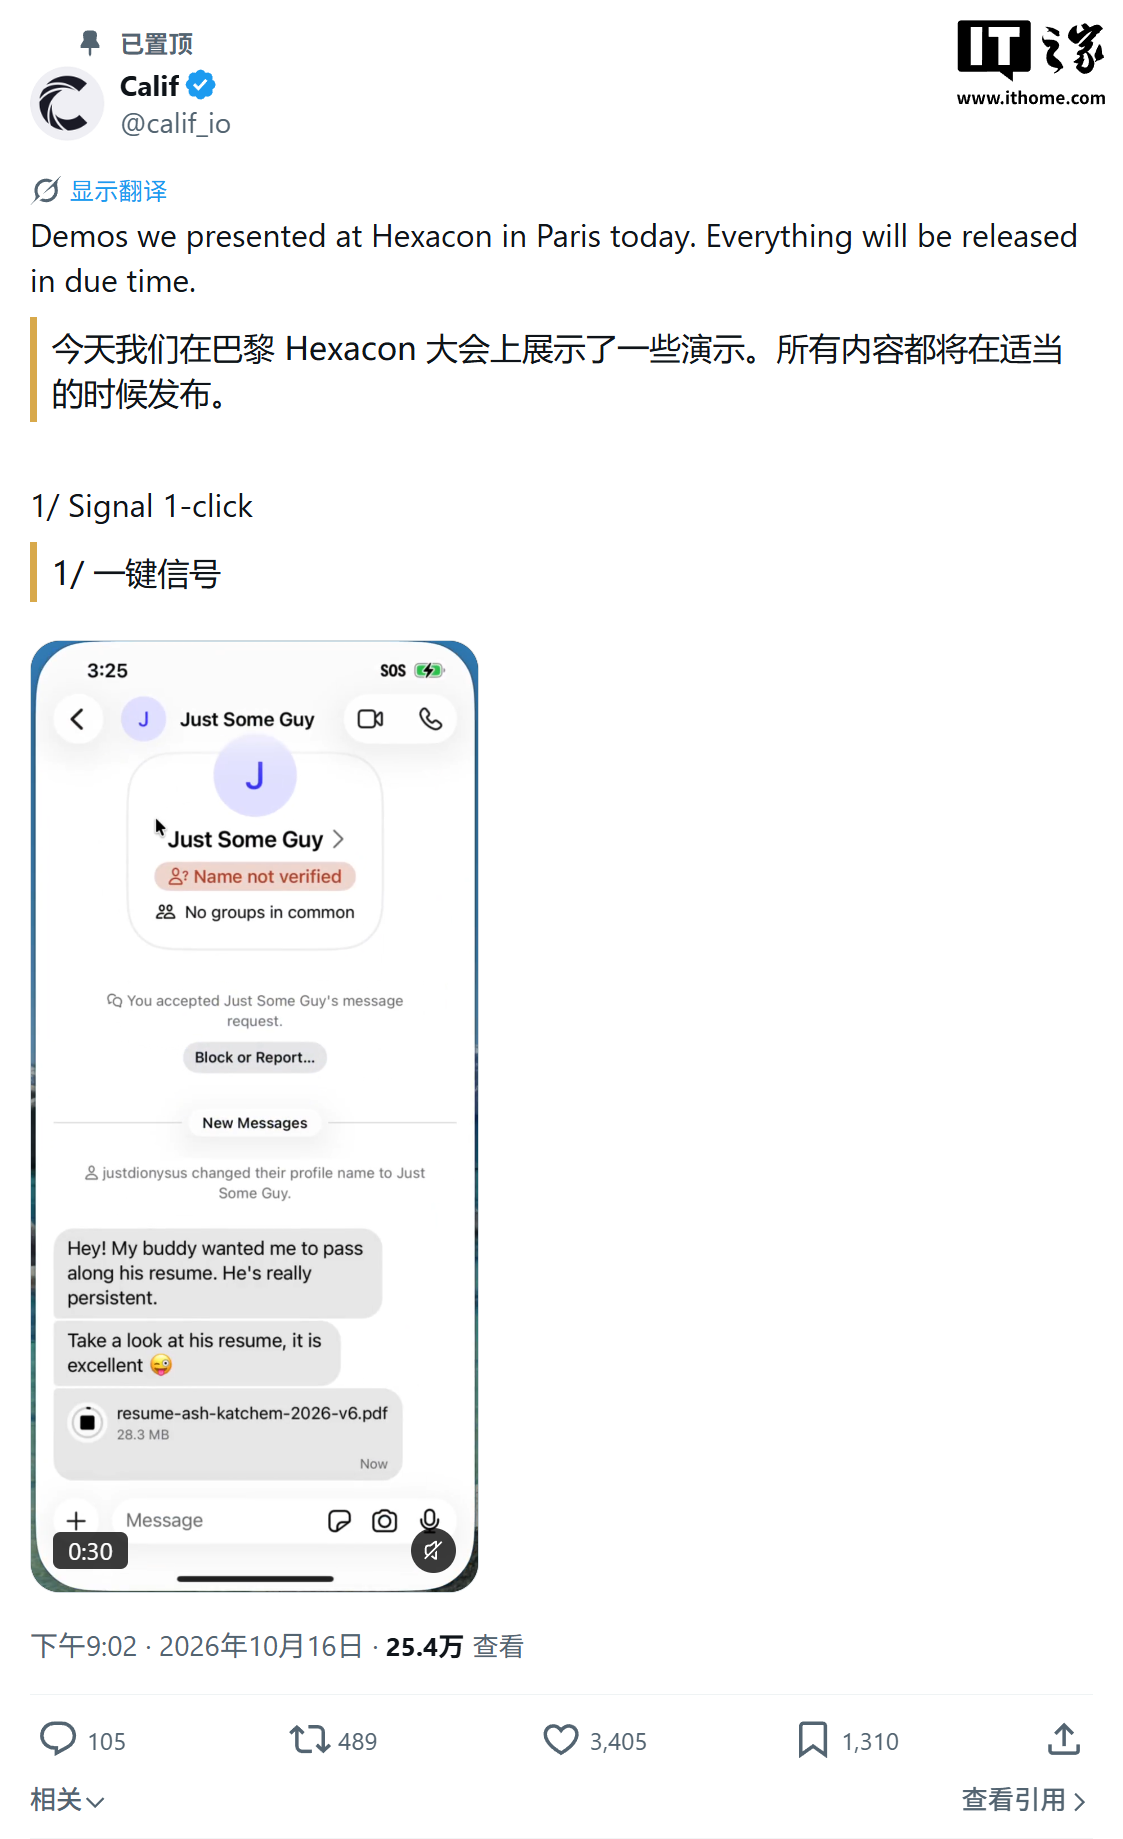
However, the public is not able to reproduce this jailbreak on their own for the time being. Calif.io has not yet disclosed the name of the vulnerability used, technical details, or downloadable tools, only stating that the relevant information "will be released at an appropriate time." The company also showcased other projects during the conference, including a one-click attack using Signal and demonstrations related to iMessage.