Knutsford, UK, November 5 (Reuters/ PR Newswire ) – The company behind Burp Suite, PortSwigger, announced today that its Burp AT for enterprises is now officially available. This is a proxy-based penetration testing solution designed to help security teams investigate critical applications more deeply and more frequently.
PortSwigger indicates that Burp AT combines specialized Burp tools, penetration testing skills jointly developed with PortSwigger Research, as well as relevant application contexts. The proxy will plan the testing methods and use the web security testing tools from Burp, making adjustments throughout the learning process.
For the AppSec leaders who have to balance test priorities with the limited capabilities of experts, Burp AT helps the team advance investigations that might otherwise have to wait, retest after changes are made to the application, and conduct more in-depth tests on a larger number of assets more frequently.
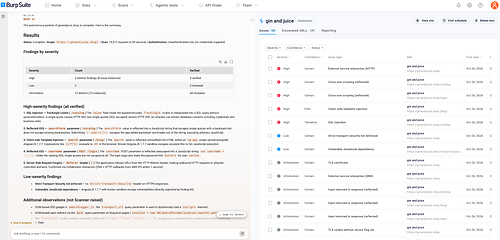
The security team can decide for themselves how much permission to grant, ranging from guided investigations to the autonomous execution of predefined tests. PortSwigger states that Burp will definitively execute the configured scope and permissions, rather than being determined by the model itself; at the same time, experts will assess the evidence to determine which vulnerabilities need to be addressed and where further investigation is required.
PortSwigger Product Manager Chris Wood stated: " Pentesters has already demonstrated what proxy-based testing can achieve in a single application through Burp AT. For the security team, the challenge is how to extend this capability to the entire application portfolio without losing control. Burp AT now allows the team to run proxy-based testing on a large scale within predefined scopes and with protective measures in place, while ensuring that they can stop it at any time and see what the proxies are doing. As a result, the team can gain this level of depth in more applications, and the control mechanisms are built-in."
Burp AT uses specialized tools and research-driven methods to help teams bring professional testing to a deeper level in more applications. It equips proxies with Burp tools used by professional penetration testers, as well as specialized skills developed by PortSwigger Research.
These specialized tools are designed to handle the abnormal traffic and unusual behaviors inherent in security testing. Research-driven techniques provide a structured approach for proxies to follow, allowing them to track promising leads and make adjustments based on evidence, thereby ensuring that organizations obtain consistent and comparable results across each application being tested.
PortSwigger Product Manager Tom Shelton - Lefley states: "The best results of proxy-based testing come from providing the right tools for the proxies, not just a powerful model. Burp AT enables the proxies to use the dedicated tools Burp autonomously and to operate under the guidance of a workflow that has been validated through practice by our researchers. In Burp AT, the orchestration layer connects these tools into a complete testing process, helping the proxies to maintain consistency across different tests by following established penetration testing methods. The proxies are responsible for reasoning, while Burp ensures accuracy; this is how autonomous testing provides the depth required by the team."
Achieving autonomy under one's own organizational conditions: An organization can decide to automate how much of the testing process, as well as in which stages the team should remain closely involved, ranging from user guidance to autonomous execution of predefined tests. Teams can increase or decrease the granted permissions based on the application, tasks, and the organization's risk preferences, and can intervene at any time when necessary.
Regardless of the level of autonomy chosen, Burp will always execute the configured scope and permissions, rather than being determined by the model itself. This means that the proxy cannot perform operations that are not allowed at the tool layer, thus maintaining the test boundaries even when more tasks are delegated. The team can still view the test activities and the evidence behind them, allowing for supervised evaluation of the results and decision-making regarding risks.
For organizations interested in learning more about Burp AT, if you wish to discuss it, please fill out the relevant form. For more information, please visit: https :// portswigger.net / burp / burp-at.
Going to San Francisco this year to participate in OWASP Global AppSec USA? You are welcome to visit the G14 booth on November 5th and 6th to meet with the PortSwigger team, and you can also request a scheduled time to communicate with them.
About PortSwigger
The mission of PortSwigger is to help protect network security around the world. Its subsidiary, Burp Suite, is an industry-standard web security testing platform that is used by over 90,000 security professionals and 18,000 organizations in more than 170 countries and regions worldwide.
PortSwigger's products cover practitioner-led testing and enterprise application security. Burp Suite Professional helps security professionals to conduct in-depth investigations of vulnerabilities, while Burp Suite DAST assists over 1,000 organizations with automated security testing in large-scale scenarios. PortSwigger also engages in strategic collaborations with global enterprises, including SAP, combining their software with pioneering security research and free practical training to drive advancements in network security practices.
For more information, please visit portswigger.net.
Media contact: Kieron Hughes, Vice President of Marketing, kieron.hughes @ portswigger.net